WNC LogoWNC
ServicesSolutionsCompanyAcademyLabsContact
Open Kanban

We No Code. We Architect.

Start a project daniel@we-nocode.com
WNC LogoWNC

AI & automation partner. Made with care across the US, Poland, Estonia, Brazil & Ukraine.

daniel@we-nocode.com+38 (068) 758-94-22+38 (095) 411-95-37
Remote-first, worldwide

Solutions

  • Atflow
  • Alt Auth
  • AdCrier
  • Pastukh
  • Olymp Hill

Portals

  • Client Portal
  • Investor Portal
  • Partner Portal

Company

  • About Us
  • Our Team
  • Case Studies
  • Testimonials
  • Investment
  • Blog
  • News
  • Careers
  • Locations
  • Contact

Labs

  • Miltech
  • AI Labs
  • Internet of Things
  • Robotics

Initiatives

  • Startup Program
  • Academy
  • Olymp Hill

Services

All services
AI
  • Agentic AI systems
  • AI agents & copilots
  • MCP servers
  • RAG pipelines
  • Voice AI agents
  • AI-native software
  • Workflow automation
  • LLMOps & evals
  • Fine-tuning & models
  • Document AI
  • Computer vision
Development
  • Web development
  • Mobile development
  • SaaS & MVP development
  • UI/UX & product design
  • Integrations & APIs
  • E-commerce development
  • Legacy modernisation
  • QA & test automation
  • No-code & low-code
  • Desktop development
Embedded & IoT
  • IoT solutions
  • Embedded firmware
  • Embedded Linux & SoC
  • Edge AI & TinyML
  • Wireless & connectivity
  • Hardware prototyping
  • IoT platform & cloud
  • Fleet & OTA management
  • Industrial IoT (IIoT)
  • IoT security
Cloud & data
  • Data engineering
  • AI cloud infrastructure
  • Server development
  • DevOps & platforms
  • Cloud migration & FinOps
  • BI & dashboards
  • Performance analytics
  • Support & SRE
Security
  • Pentesting
  • AI red teaming
  • Compliance readiness
  • Auth & identity
  • Cloud security
  • Secure SDLC
  • Supply-chain security
  • Security audits
  • Security monitoring
  • Zero trust
  • Privacy & GDPR
Advisory
  • Consulting & advisory
  • CTO-as-a-service
  • AI strategy & governance
  • Technical due diligence
  • Dedicated team
  • AI training for companies
R&D / innovation
  • Proof of concept & feasibility
  • Rapid prototyping
  • Applied AI research
  • Technology discovery & scouting

© 2026 WNC. All rights reserved.

🇺🇦Stand with Ukraine

We No Code

All services

IoT security

Ship devices that can’t be cloned, hijacked or recalled.

Security for connected products, from secure boot to the audit.

A connected product is only as safe as its weakest device in the field. We secure the whole chain: secure boot and a hardware root of trust, per-device identity, encrypted transport and signed updates. Your devices and their data can’t be cloned, hijacked or quietly recalled, and the product passes the audit instead of becoming the headline.
Let’s manage Open Kanban
An abstract render of a secured connected hardware device

01 / What it gives you

From the silicon up to the audit.

01

Firmware that only runs if it’s yours

Secure boot and a hardware root of trust, so a device starts your signed firmware and nothing else. Tampered code never gets to run.

02

An identity no one can clone

Every device carries its own certificate from your PKI, so a leaked key compromises one unit, not the whole fleet.

03

Data that stays private in transit

TLS and mutual TLS on every link, so traffic between device and cloud can’t be read, spoofed or replayed.

04

Updates that can’t be tampered with

Signed, verified over-the-air updates so a hijacked update channel can never push someone else’s code to your devices.

02 / Stack

The technology we build with.

Industry-standard, boring in the good way: tools with a future, that the next engineer will know too.

Device trust

  • Secure boot

    Firmware signed and verified at boot

  • TPM / secure element

    Keys held in a TPM or secure element

  • PKI

    Per-device certificates from your own PKI

  • mTLS

    Mutual TLS so both ends prove identity

Communication

  • TLS

    Encrypted transport for every link

  • Signed OTA

    Firmware updates signed end to end

  • Certificate rotation

    Certificates rotated before they expire

  • VPN

    Private tunnels for fleet backhaul

Assurance

  • Penetration testing

    Hands-on attacks before you ship

  • Threat modelling

    Risks mapped while it’s still a design

  • ETSI EN 303 645

    Built to the consumer IoT baseline

  • CRA compliance

    Ready for the EU Cyber Resilience Act

03 / Approach

How we build things that last.

01

Trust rooted in hardware

Secure boot and a hardware root of trust mean a device only runs firmware you signed. Tampered or swapped code never starts.

02

An identity per device

Each unit gets its own certificate from your PKI, so a stolen key costs you one device, not the fleet.

03

Updates you can trust

Signed, verified OTA so a compromised update path can’t turn your devices into someone else’s botnet.

04

Proven, not assumed

Penetration testing, threat modelling and compliance mapping, so security is something you can show an auditor rather than just claim.

04 / Standards

Best practices we don’t skip.

We adhere to industry standards and proven methods on every project — they are what makes the estimate hold.

  • Verify firmware at boot from a hardware root of trust
  • Store device keys in a TPM or secure element, never in flash
  • Give every device its own certificate and revoke it cleanly
  • Encrypt every link with TLS, and use mutual TLS where both ends matter
  • Sign OTA updates and verify them before they install
  • Rotate certificates automatically, before they expire
  • Threat-model device, cloud and companion apps, AI features included
  • Map the build to the EU Cyber Resilience Act, ETSI EN 303 645 and NIST IoT: SBOM, vulnerability handling, a stated support period

05 / Infrastructure

Where it runs, and how it stays up.

  • Secure boot and key storage in a TPM or secure element
  • Per-device PKI with clean issuance and revocation
  • TLS / mTLS transport and signed, verified OTA
  • Penetration testing and ETSI, NIST and CRA compliance mapping

Good questions

What clients ask us

Straight answers to what buyers ask before they start.

Yes. WNC maps connected products to the Cyber Resilience Act: secure-by-design firmware, an SBOM per release, a vulnerability-handling process with timely reporting, signed OTA updates and a stated security-support period.

Related work

Where we’ve done this

Projects and products of ours that involved this service.

Hirske Dzherelo
IoT · Manufacturing

Hirske Dzherelo

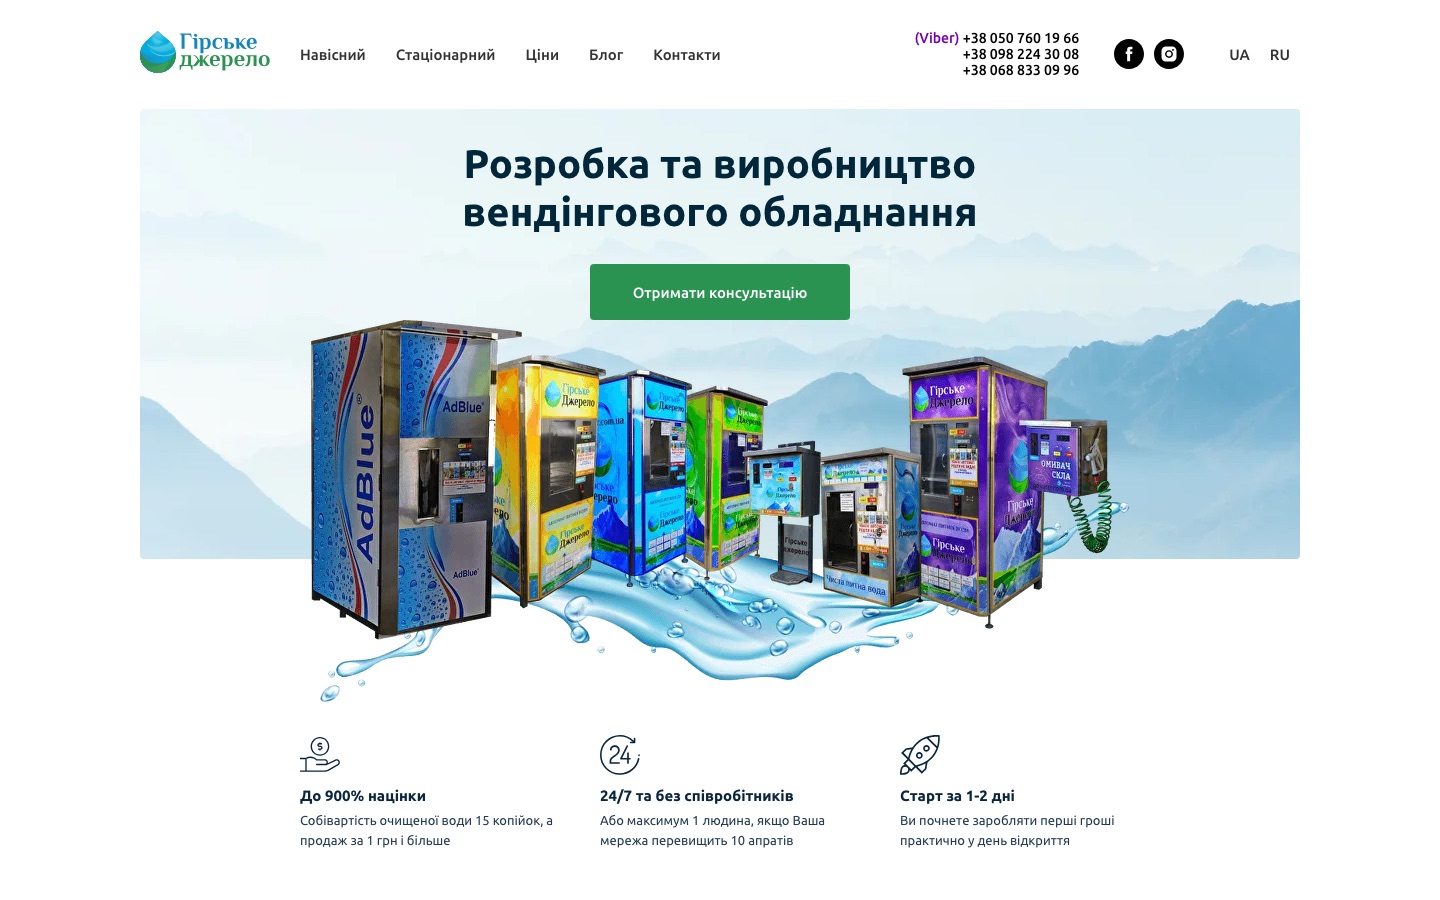
IoT for a factory that builds drinking-water vending machines: every machine reports to the server every 3–5 seconds and is monitored and tuned remotely from a web cabinet and a Telegram bot.

IoT · TelecomIoT service intelligence platform for mobile operators
IoT · Telecom

IoT service intelligence platform for mobile operators

From connectivity to intelligence: a platform that sits above an operator’s existing systems and turns fragmented SIM, device, traffic and service data into enterprise-facing visibility, trust and action.

Start

Ready to secure your devices before someone else does?

Tell us about your product and where you’re worried. A senior security engineer, not a sales rep, writes back.

Let’s manage IoT platform & cloud